On November 6, 2026, Singapore's CSA, GovTech and IMDA issued a joint advisory on personal AI agents. The reviewed document contains five steps: limit access, control important actions, understand data handling, protect against misuse, and consider effects on others. It is consumer guidance, not a new ban or proof that the applications it mentions are secure.
Permissions need technical boundaries
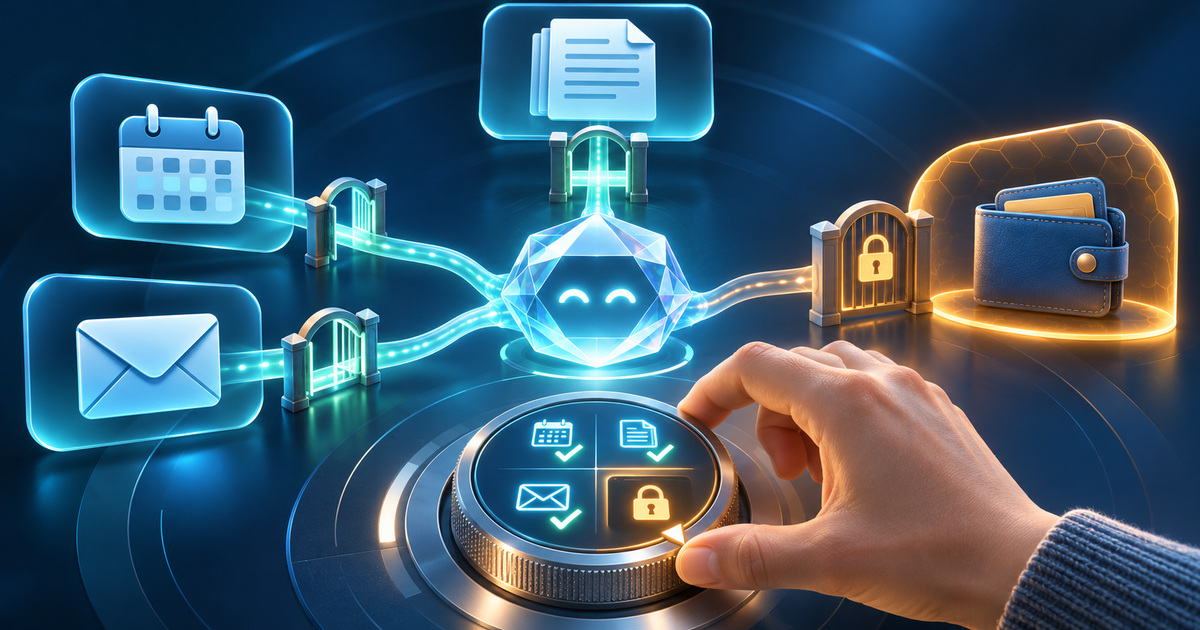
The document recommends narrow permissions, separate approval for consequential actions and technical controls in applications. A chat instruction alone is insufficient as a boundary.
Our editorial interpretation is that users need a comprehensible description of every connection: what can be read, what can be changed, and how access ends. A single “connect” button does not adequately explain those different capabilities. Before trying a service, a person should be able to describe exactly what they are authorizing.
An email and calendar example
Suppose an assistant is preparing a meeting proposal. Seeing available time slots and producing a draft may be enough. Sending to every participant, deleting an older event or accessing the entire archive are separate actions. This is our scope-design example, not a promise that a particular service exposes exactly these separate controls.
A useful trial would start with nonsensitive content. The user can compare the proposed date and recipients with their actual intention before permitting a real send. A misunderstanding is then caught in the draft, where correction is easy, rather than after a message has reached other people.
There is a second question: what happens after the task ends? A person should know whether a connection stays active and whether another task can reuse its permissions. Without that clarity, “I will ask” in one conversation does not reliably describe the future behavior of the whole service.
Convenience and accountability belong together
In our assessment, a good interface would distinguish completed actions from intended ones. “I will send” and “sent to these recipients” are different states. When an outcome is uncertain, establishing what actually happened is more sensible than immediately repeating the action. This is an editorial product-evaluation criterion, not a comparative test we have conducted.
The advisory is also useful to Bulgarian readers as a starting point for questions to providers. Singapore's agencies do not certify that every service can be configured in the same way. For a particular application, check its current controls and the actual scope of its connections. SIExpo is not offering a legal assessment or claiming that reading the guidance eliminates technical risk.
Editorial verification: 2026-11-08T17:56:23.508205+00:00.