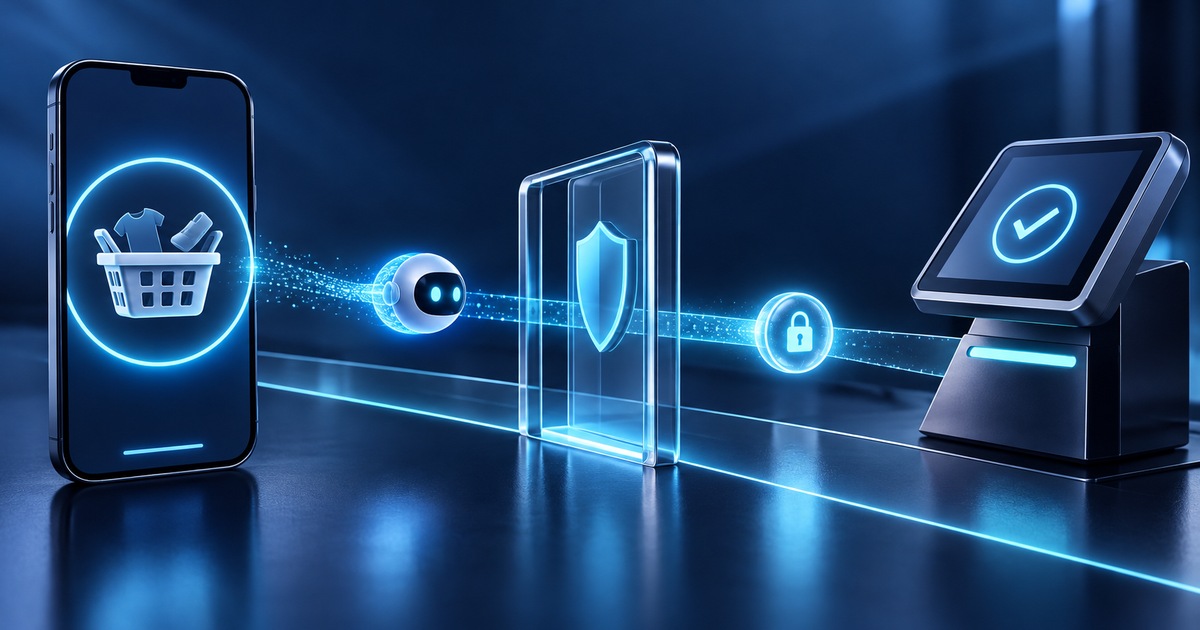
On 13 October, American Express published Intent Intelligence: confirmed customer intent would reach the card issuer before an AI agent buys something. The public framework does not establish a universally adopted payment-network standard.
From conversation to an authorized transaction
The announcement describes confirmation, an Intent ID and Proof of Intent Token, a scoped payment credential and subsequent checks. ACE Developer Kit integrations remain under development.
The distinction has practical value. A model's ability to find a suitable item does not establish whether the customer authorized that particular transaction. Conversations include preferences, uncertainty and examples; a payment control needs to know what was finally approved. Our interpretation is that this boundary must be visible to the customer before the agent acts.
What proof of intent carries
Amex's technical article describes the token as a JWT containing high-level constraints. Intent may include an amount ceiling, expiry, merchant and transaction count, with updates and cancellation contemplated. It proposes removing personal details unnecessary for purchasing from the shared summary. These are documented design rules, not measured evidence of fewer disputes.
Consider a hypothetical request to buy office supplies within an overall budget. An agent could choose a cheaper item but add a subscription. A low initial price would not, by itself, establish compliance with the assignment. This is our example: meaningful authorization needs to capture the material conditions and the confirmation screen needs to present them clearly.
Signed data is not the entire solution
A signature can help establish a message's origin and integrity. It does not prove that the intended purchase was correctly understood in the first place. If the customer confirms an ambiguous summary, protected transmission preserves the same ambiguity. Evaluating the interface and evaluating transaction enforcement are therefore separate jobs.
In our proposed test, an agent first displays the exact amount, number of purchases and expiry. The assessment would then cover altered conditions, an expired authorization and a repeated attempt following an interrupted response. The system needs to determine whether the transaction already happened before repeating it. These are evaluation criteria, not a claim that we integrated with Amex.
Control and information access
A customer should be able to inspect active authorizations and their outcomes. An operator needs enough information to investigate without making the entire personal conversation part of a payment log. Where several participants are involved, it is useful to identify who holds the current intent and who applies an update or cancellation.
Publishing the framework is a concrete development in agentic payments. A successful implementation still needs answers about compatibility, constraint coverage and actual failure behavior. SIExpo does not claim that disputes disappear, that every merchant already supports the approach or that it guarantees a correctly selected product.
The same distinction applies when judging future demonstrations: a completed checkout proves one execution path. It does not establish what happens when the agent changes its plan or the customer withdraws permission. Those boundary cases should have explicit outcomes before a service is described as reliable.
Sources were read on 14 October 2026 between 09:25 and 09:35 Europe/Sofia. Assessments and proposed checks are editorial analysis; SIExpo has not independently tested the product. The cover is an AI illustration, not a photograph of an actual event.