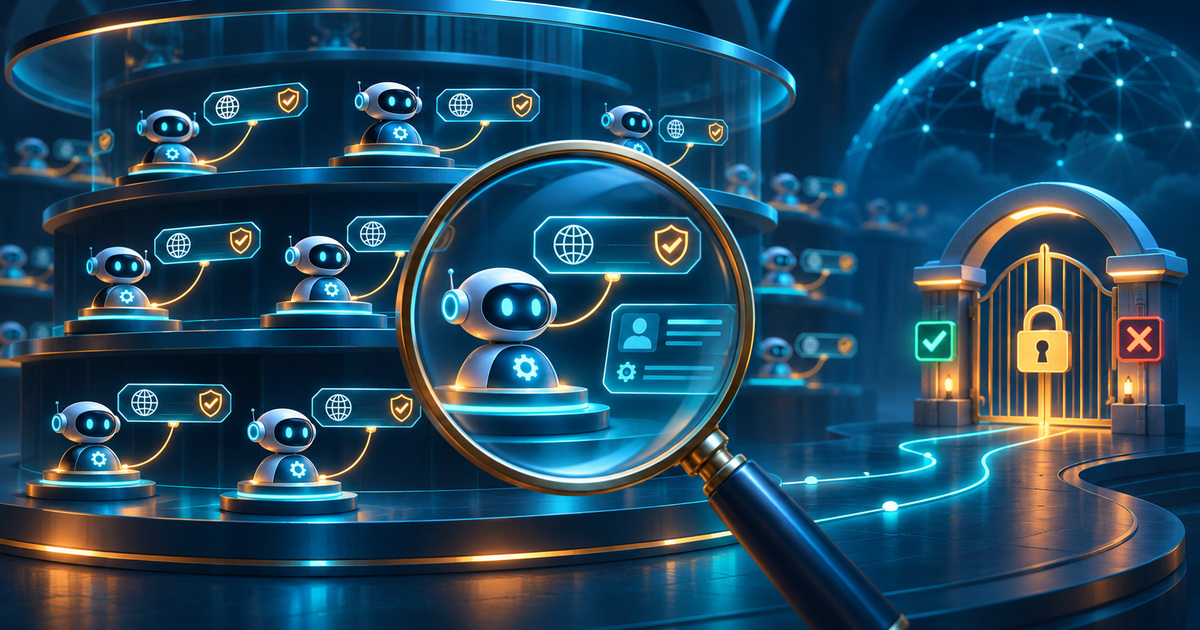
On November 20, AWS announced verified domain names and public discovery for agents and AI tools in Agent Registry. Publishers can prove domain ownership and associate names with their resources. Published records are searchable by AWS-authenticated users through semantic and lexical search. Discovery can consequently extend beyond one registry and account; it does not mean anonymous access to every tool.
The problem a catalog addresses
In an organization with many agents, finding an existing capability can become a task of its own. Teams need to know what exists, what it does and who maintains it. Official documentation describes a catalog for agents, MCP servers, tools and other resources, with publication and approval workflows for records.
Domain association adds a verifiable provenance signal to a public record. That is useful within a specific scope. Establishing that a publisher controls a domain differs from establishing that its tool is appropriate for a particular business task.
A catalog also separates describing a resource from operating it. The record can tell a consumer where to look and what the publisher says the resource does. The behaviour of the underlying service still needs to match the consumer's actual requirements.
Identity, description and behaviour
Consider an editorial example: an invoice-preparation agent discovered through a catalog description. A verified domain could help distinguish the genuine provider from a similar name. Other questions remain: which data does the tool require, what does it return, and should it be permitted to write into the accounting system? Registration alone does not answer them.
Semantic search supports discovery rather than final suitability assessment. A closely matching description could refer to another version, region or workflow. Exact terms help locate a named capability, while descriptive text adds context. Both still need to be compared with the real requirement.
This is particularly relevant when two resources use the same broad label. Drafting an invoice, validating it and committing it are different operations even if all are described as invoice automation. A useful evaluation preserves those distinctions rather than treating a search match as a complete integration decision.
Discovery comes before authorization
Three decisions should remain separate: whether a record is visible, whether an organization approves using the resource, and what an agent may actually do during execution. Combining them into one general sense of approval can hide important boundaries.
The documentation describes publication, curation and discovery roles in the catalog. Permissions to underlying services and data form another layer. The ability to find a tool should not be presented as automatically expanding its operational access.
What a catalog consumer should examine
Before integration, useful questions concern the maintaining organization, purpose, conditions and execution boundary. In the invoice example, a reviewer would distinguish a proposed draft from a final accounting entry. These are different products from the user's perspective, even when their descriptions sound similar.
Quality assessment needs a representative scenario and expected outcome. Verified identity removes one uncertainty—provenance—but does not replace testing. Maintenance raises a related question: which version was evaluated, and how will later behavioural changes become visible?
An organization can also record why a resource was accepted for a particular workflow. That decision need not apply to every other workflow. Keeping the intended purpose next to the approval makes reuse more precise and helps avoid treating an old decision as unrestricted permission.
Public records could make existing work easier to reuse. Unclear or outdated descriptions could instead create more verification work. Metadata quality and maintenance therefore matter alongside the search mechanism. This is editorial analysis, not a measured adoption result for the service.
AWS Agent Registry's update is interesting as infrastructure for finding agents and clarifying their origin. The useful boundary is that a verified domain, a discovered resource and an authorized action are different things. The catalog supports the early steps; dependable use continues with suitability assessment and specific access decisions.