Singapore-based Flexxon announced on November 10, 2026 that it had been selected for CyberCall 2025 funding for an AI-agent security project. X-PHY AI Armor is proposed as an MCP gateway with hardware-rooted authorization for sensitive operations. The announcement concerns supported development. It does not establish that a finished product has already been deployed and independently evaluated by customers.
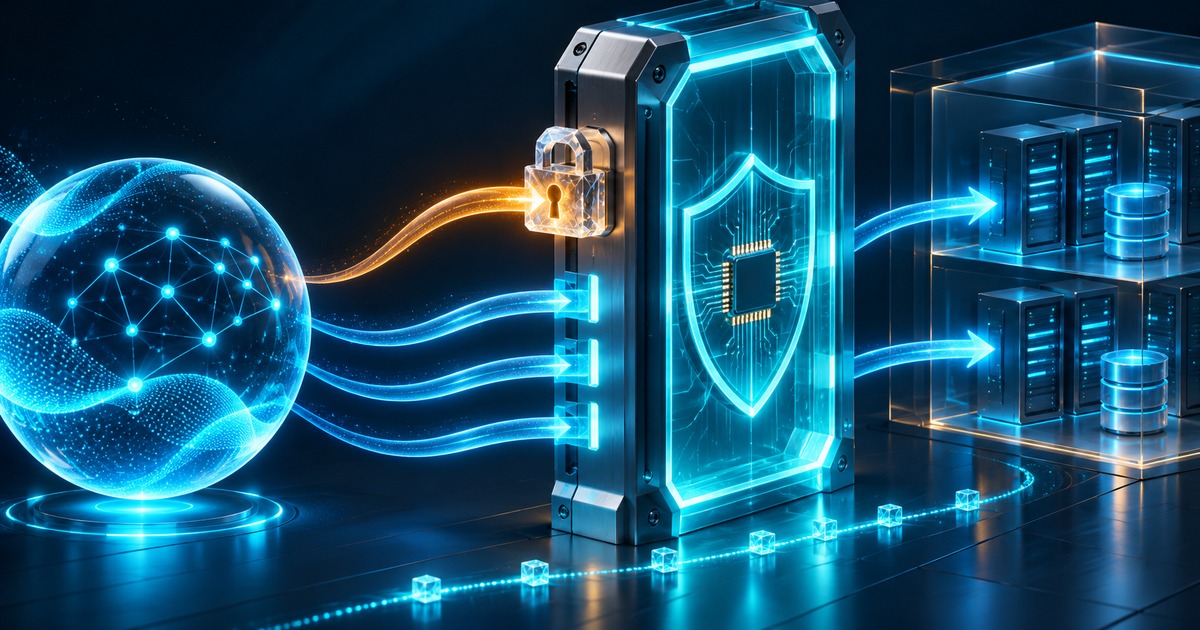
The company describes an intermediary between an agent and the systems it accesses. High-risk actions would be checked by a device, with decisions retained in a hardware-protected audit trail. Claims that a compromised host could not alter the decision or erase its trace are the manufacturer's proposed protections. We are not presenting them as results established by SIExpo.
Why a separate boundary matters
An agent can have valid service credentials and still propose an inappropriate action. An illustrative example is an assistant treating instructions inside a document as a new task. This is our example of the problem, not a particular breach attributed to Flexxon.
The official Model Context Protocol security guidance separately addresses user consent, token validation, sessions and minimizing scopes. A protocol for connecting tools does not make every invocation a correct business decision. It forms part of the communication path on which specific restrictions need to operate.
OWASP likewise treats risks in language-model applications as more than the quality of a textual response. In this context, our interpretation is that a useful protection needs to follow the consequences of tools. A well-written recommendation and an actual database change have different scopes.
What a future product needs to demonstrate
The first evaluation question is which operations pass through the boundary. If some tools use another route, describing the entire agent as protected could be too broad. An implementation needs a clear account of the enforced boundary and the external systems outside it.
The second question concerns policy definition. Hardware may make a decision harder to alter without establishing that its rule was appropriate. In a hypothetical pilot, we would test permitted reading, prohibited transmission and an action requiring separate confirmation. This separates effective enforcement from sensible permission design.
The third question is failure behavior. When a device or its connection is unavailable, an operator needs to know whether the task is refused, queued or moved into another mode. These choices have different availability costs. They should be tested before production traffic rather than inferred from a general description of protection.
The audit trail is another part of the evidence. A useful record connects the request, the applicable rule and actual execution. A durable refusal record does not automatically establish whether an external operation already in flight has completed. This is our proposed evaluation criterion, not a discovered defect in an unreleased product.
Funding and readiness are different developments
CyberCall supports the development of solutions. Selection establishes a supported project, not delivery terms, independent validation or complete documentation. We are not announcing a general-availability date, a price or a percentage of attacks prevented: the verified announcement does not establish those outcomes.
Nor should a hardware boundary be interpreted as removing the need to control the agent's existing access. In a proposed assessment, the team would still document the accounts, tools and information the agent can reach. That inventory makes the protected scope testable. Otherwise, a successful demonstration might cover only the selected example rather than the intended workflow.
The significance is the direction toward separating authorization from the environment where an agent operates. Whether this implementation fulfills its promise depends on tool coverage, policy management and demonstrable failure behavior. Those are the concrete next questions for the development program, while the funding announcement remains the verified event today.
Sources: Flexxon — CyberCall funding for proposed X-PHY AI Armor, MCP — official security best practices, OWASP — LLM application security risks. The cover is a conceptual AI editorial illustration, not a documentary photograph.
Editorial verification: 2026-11-10T17:08:25.417687+00:00.