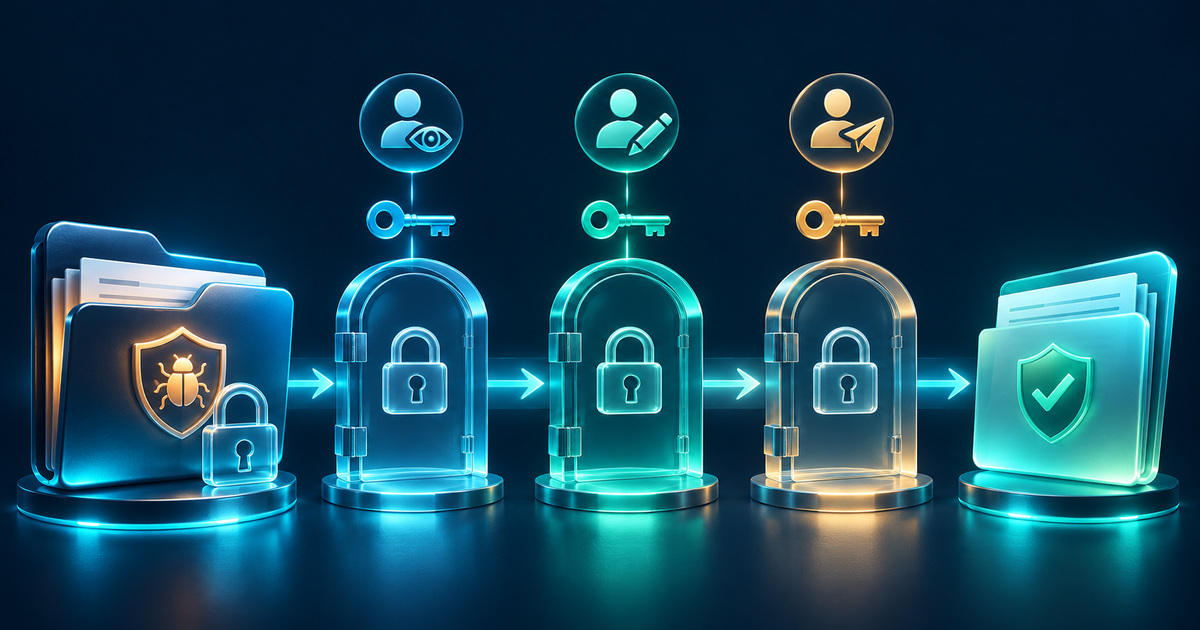
On November 20, GitHub announced general availability of security-advisory permissions in custom repository roles. Viewing, management, accepting private reports and publication with CVE requests can be separated. Access is assigned to the required repositories on plans supporting custom roles. This is not a universal change for every free account.
Restrictions remain: merging from a temporary private fork requires an administrator or security manager. Documentation also describes inherited base-role permissions. A new narrow permission therefore does not automatically reduce access someone already receives through another route.
Why this matters for AI findings
Our editorial interpretation is that finding a possible problem and having authority to disclose it should be separately manageable. An automated tool may suggest something for investigation without gaining grounds to announce a vulnerability or assign an identifier to its own claim.
For a team receiving many reports, separation helps define consecutive responsibilities: reviewing evidence, checking reproducibility and coordinating publication. Those roles alone do not prove that the workflow is sound. Actual access still needs inspection, including the routes by which a person can acquire broader powers.
A proposed pre-deployment check
We would create a test repository with a non-sensitive example report. Then separately check what each role sees, whether it may add a collaborator and who may publish. The aim is to establish effective access rather than merely a setting on one screen. This is our proposal, not a test conducted in the user’s organization.
For an AI-assisted tool, we would limit its input to necessary evidence and retain a human disclosure decision. A rejected hypothesis should remain clearly rejected so that another report cannot later recycle it as a confirmed problem.
When team membership changes, check whether previous access actually disappeared. Inherited roles, other group memberships and earlier grants can make the effective boundary wider than expected. A list of role names is insufficient evidence by itself.
We would also rehearse handing a report to another maintainer. A useful record needs the current evidence, unresolved questions and next authorized action. Without those, a transfer may create duplicate investigations or an accidental premature announcement even when individual permissions are correctly configured.
The release supplies a finer tool for separating responsibilities. Its value depends on correct role assignment, checks against actual operations and a clear distinction between an unconfirmed AI finding, a verified vulnerability and an authorized public advisory. None of those stages should be inferred merely from the existence of the previous one.