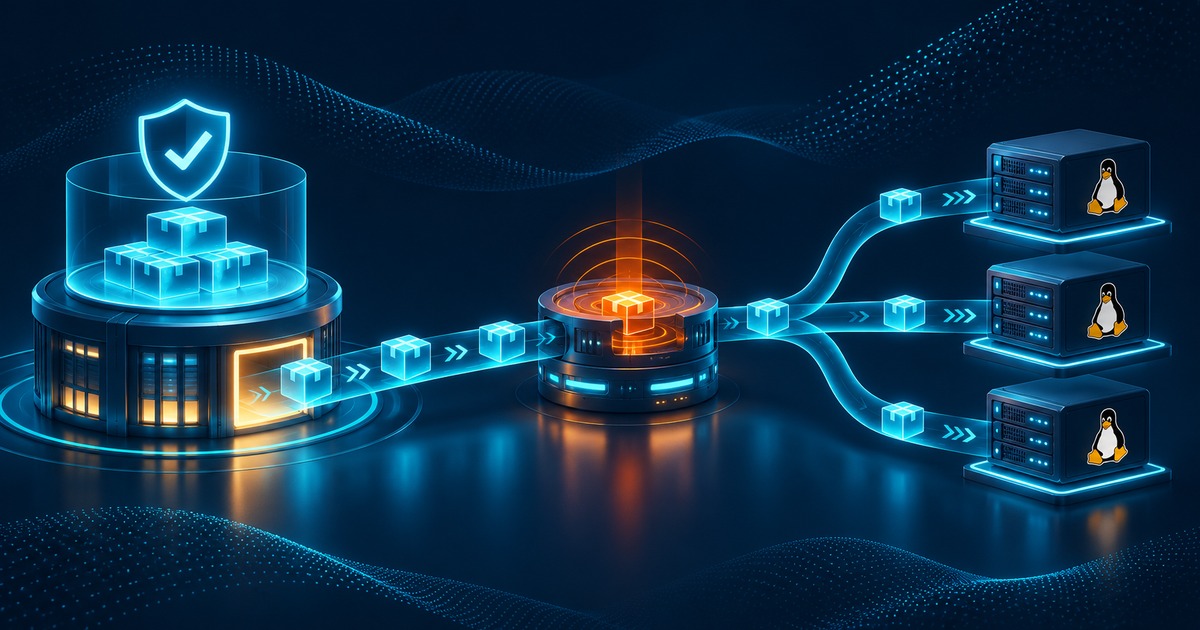
On November 3, 2026, OpsShield disclosed that an attacker had used the company's update infrastructure to distribute a tampered cPGuard package. The product protects Linux web servers in hosting environments. In its later disclosure, the vendor estimated that about 2,950 customer servers ran the fake update. Separately, it identified about 7,900 billing portal accounts whose records were exposed. The figures describe two different groups, according to the company's investigation.
How the vendor reconstructed the incident
OpsShield traces the first activity against its portal to November 1. The attacker registered a customer account and later gained the ability to run commands on the billing and licensing server. The company says an update publishing key was stolen. Its logs do not show the exact request that enabled the initial access. The vendor patched two potential entry points and continues to review the relevant components.
The later timeline places execution of the fake update between 02:08 and 03:20 UTC on November 2. The earlier bulletin identifies versions 5.88.12 through 5.88.19, inclusive, as affected and notes that servers check for updates at different intervals. A log entry showing an affected version was installed is a reason to treat the machine as potentially compromised. The entry alone does not show which data was read or transferred.
What information was exposed
The package ran with root privileges. OpsShield says the data it sought included local account password hashes, private SSH keys, database credentials and administrative shell history. On a small number of servers, cloud storage keys were also exposed. Shell histories and configuration files can contain secrets that can be used directly. Password hashes are a different type of data, with risk depending in part on how difficult the password is to recover.
The vendor separately reported that billing portal records were copied, including names, company details, addresses, emails and passwords stored as bcrypt hashes. The early notice mentioned 32 files then known to have been retrieved from a vendor server. The later estimate of about 2,950 refers to machines that ran the package. These figures measure different things and do not identify the individual files taken from each machine.
Updating and replacing credentials address different risks
The initial bulletin identifies 5.88.25 as the minimum corrective release. The later disclosure describes 5.88.26 as a clean update that removes the hidden shell and a follow-up update that removes a scheduled task. OpsShield advises installing the latest available version and checking that the known traces are gone. Their absence after cleanup cannot establish whether the package ran before the update.
An update cannot invalidate credentials that were already copied. For potentially affected machines, the vendor recommends changing passwords and tokens from a trusted environment, replacing SSH keys and removing the old public keys from every system that trusted them. When direct manual access is confirmed, the vendor recommends rebuilding from a clean backup made before November 1. For billing portal accounts, the separate advice is to reset the password and enable two-factor authentication. OpsShield comments on the general role of AI in speeding up attacks, but provides no evidence that this attacker used AI.