Cursor published additional findings on November 13 about the security incident investigated since October. The company describes a chain involving a key exposed at vendor Fireworks, access to historical coding-agent traces and subsequent use of credentials found in that material. This is Cursor's reconstruction, not a forensic conclusion independently reached by SIExpo.
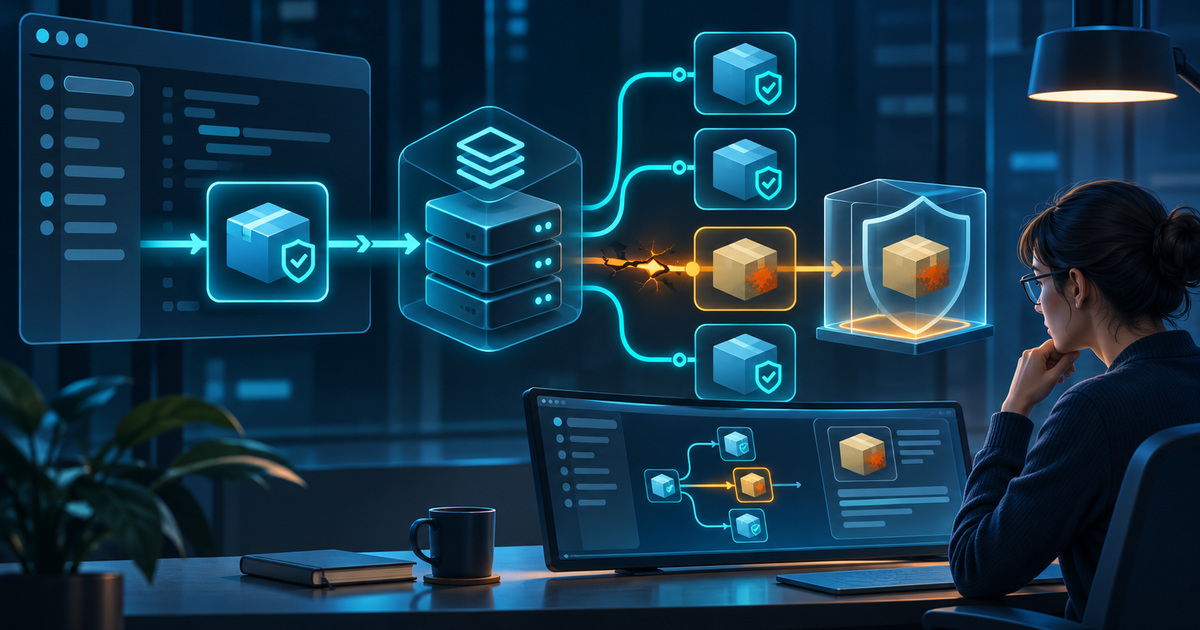
According to the update, unauthorised copies of Anthropic.claude-code were placed directly in the cache serving Cursor's extension marketplace on October 29. It identifies versions 2.1.312 and 2.1.313 and an exposure window of approximately eleven hours. Cursor estimates up to 5,000 potential recipients. That is not a count of devices proven compromised. The company explicitly distinguishes the event from an official Anthropic publication and from the Open VSX source marketplace.
The original security notice provides more specific defensive guidance. It concerns affected Windows and macOS copies and describes attempts to establish persistent unauthorised SSH access. Simply uninstalling the extension may leave persistence mechanisms behind. The notice recommends reviewing available telemetry, isolating hosts where execution is evidenced and rotating credentials accessible from affected systems using a trusted machine. The official page contains checks and remediation materials. We have not run those scripts or diagnosed any reader's computer for this report.
Fireworks provides a separate account. Its November 9 update describes impacts to categories of customer information and, for a limited group, datasets and incomplete model weights. It reports work with Unit 42 and continued monitoring. That establishes a separate investigation, not independent certification of every detail in Cursor's reconstruction. The organisations are describing different systems and access boundaries, which should not be collapsed into a single undifferentiated claim.
For the AI sector, the incident illustrates why operational security needs to follow data through its lifecycle. A coding-agent trace may be treated as diagnostic material, yet its contents deserve careful classification like any other business record. SIExpo's editorial interpretation is that organisations should map the source project, logs, shared datasets and service providers separately. A promise concerning one part of a service should not automatically be applied to every other data flow. This is a suggested review method, not an additional finding about the incident.
The same reasoning applies to extension distribution. A familiar publisher name and version number do not alone establish the contents of a particular package received by a device. An internal assessment can examine installation time and channel, package identity and observed endpoint behaviour together. Those are general defensive criteria. They do not imply that every Cursor or Claude Code user was affected, nor that a version string without the distribution context proves compromise.
Organisations can make a more useful next decision by comparing the official notification with their own records instead of drawing a verdict from a headline or percentage. Distinguishing potential package delivery, actual execution and subsequent access produces a more precise assessment. Public claims remain bounded by the participating companies' investigations and may change as further evidence emerges. That uncertainty should remain visible alongside the concrete versions, channel and defensive actions already disclosed.
Editorial verification: 2026-11-15T17:59:15.509180+00:00.