xAI published version 1.21.0 of its official Python SDK on October 23, 2026. The release adds safety_identifier and guidelines to chat.create and extends compatibility to protobuf 7. When checked on October 24, the concrete change concerned the client library. It is not an announcement of a new Grok model and does not automatically establish a safer application.
Two different settings
Source documentation describes safety_identifier as a stable opaque end-user identifier, suggesting a hash of an internal ID instead of an email or display name. guidelines configures decline behavior for nsfw, violence and profanity categories; omitted categories retain defaults. An unknown category or behavior raises client-side ValueError. These are request parameters, rather than permissions for operations in an external system.
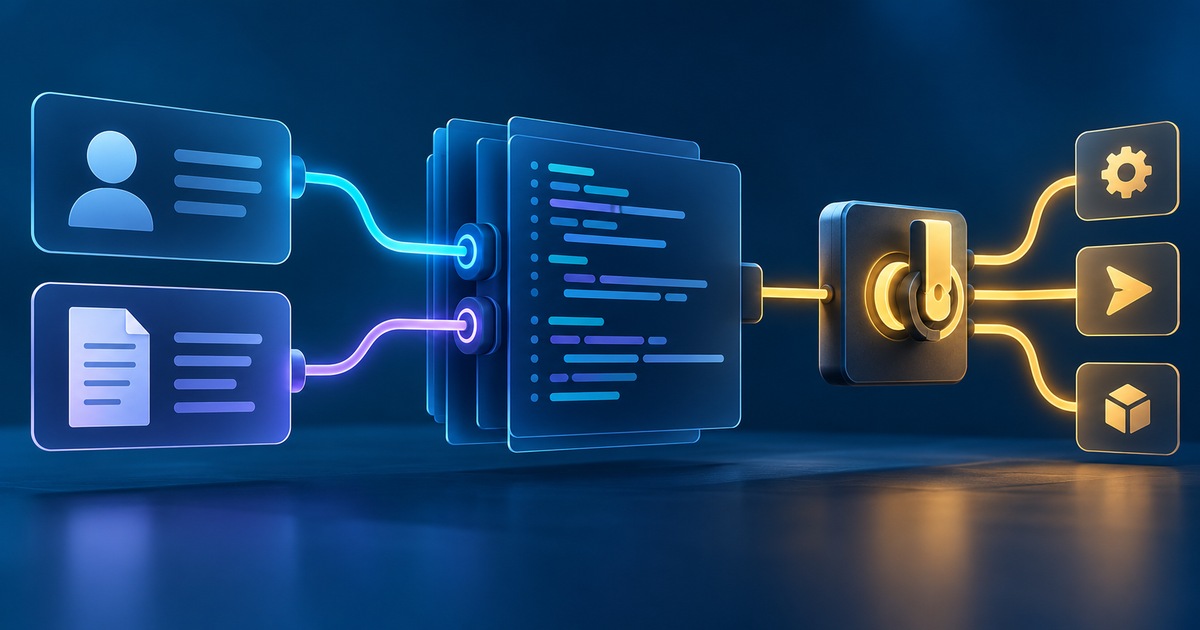
In our editorial assessment, the two settings should have different owners within an application. One associates requests with a particular user in a predictable way. The other specifies handling for certain output categories. Combining them into one generic “security” setting would make an error harder to investigate: the problem might involve identity, content or the subsequent action.
Checking an upgrade
We suggest starting migration with configuration checks in an isolated environment. For a small assistant connected to a ticket system, for example, we would record which categories are explicitly set and which remain at default. We would test a misspelled category separately from an absent setting. This is a proposed application test, rather than a claim that SIExpo sent xAI requests or measured filtering reliability.
For the identifier, the question is how the application defines stability. In our example, temporarily changing browsers should not turn one internal user into unrelated records. Meanwhile, test and production profiles should be distinguished in the team’s own documentation. We suggest recording that decision before deployment so the team can explain the relationship between a reported incident and the actual sequence of requests.
A model response does not grant action rights
Suppose the assistant proposes closing a support ticket. The output-content setting does not establish whether that particular person may close that particular record. In our proposed design, the application checks permission for each action and verifies current state before writing. If the record changes between proposal and execution, the action must be considered again rather than silently relying on the older state.
Content tests and permission tests can consequently be assessed separately. A category-based refusal does not establish correct access control; permitted text does not establish that an operation is authorized. This is our engineering interpretation of integration, rather than a promise made by the SDK release or a security result demonstrated in this article.
The practical value of this version is an explicit Python-client interface for particular settings. For an operational product, a useful next report would identify the library version, actual configuration and acceptance-test results. SIExpo checked the published release and source code without paid API calls, end-user identifiers or its own measurements of moderation outcomes. The boundaries between documented behavior and proposed application checks remain explicit throughout this report.
*Cover: conceptual AI illustration, not a documentary photograph.*
*Editorial verification: 2026-10-24T16:31:42.890381+00:00.*